Dear Valued Customers and Partners,
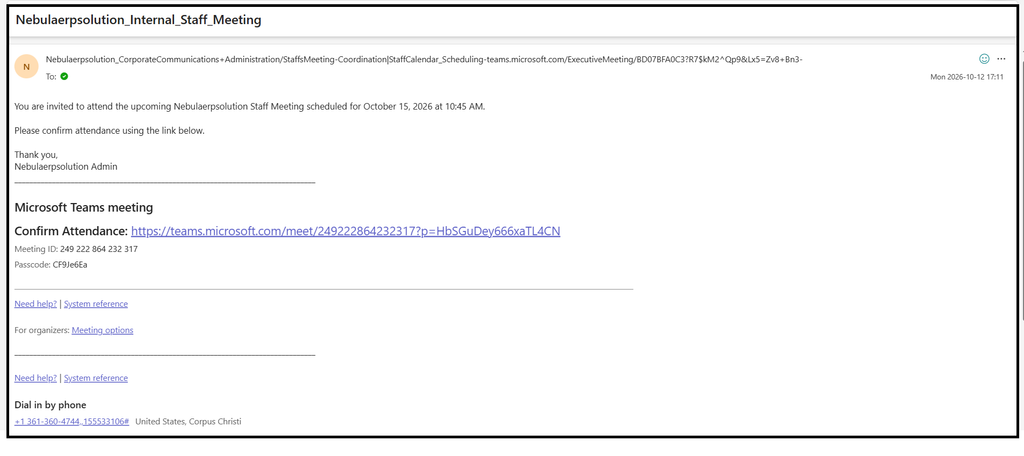
We would like to bring to your immediate attention a suspected phishing email currently circulating, disguised as a legitimate Microsoft Teams meeting invitation.
We recently received a suspicious email that appeared to originate from Nebula ERP Solution, inviting recipients to attend an internal staff meeting and requesting them to click a link to confirm attendance.
Please be aware that this email was NOT sent or authorized by Nebula ERP Solution.
More importantly, this type of scam is not limited to impersonating Nebula ERP Solution. Scammers may impersonate ANY company, including your own organization, by using similar company names, email addresses, domains, or meeting invitation formats to make their messages appear legitimate.
What You and Your Team Should Watch Out For
- Fake Microsoft Teams Invitations – Emails that closely resemble genuine Teams meeting invitations, including meeting IDs, passcodes, and Microsoft-style formatting.
- Company Name or Domain Impersonation – Scammers may use your company’s name, a lookalike domain, or a misleading sender address to gain your trust.
- Unexpected Meeting Invitations – Be cautious of meeting requests from unknown senders, even if they appear to come from your colleagues, management, customers, or trusted business partners.
- Suspicious Links – Do not click links or provide Microsoft 365 credentials unless you have independently verified the invitation’s authenticity.
Recommended Precautions
- DO NOT CLICK suspicious or unexpected links, even if they appear to be legitimate Microsoft Teams links.
- VERIFY unexpected meeting invitations directly with the organizer through a trusted communication channel.
- CHECK the actual sender’s email address and domain carefully. A familiar display name does not guarantee authenticity.
- REPORT suspicious emails to your internal IT department immediately.
- IF YOU HAVE ALREADY CLICKED and entered your login credentials, contact your IT administrator immediately for assistance.
We strongly encourage all customers to share this security alert with your entire organization, including management, finance, sales, warehouse, production, and administrative teams.
Cybersecurity is everyone’s responsibility. A single careless click could potentially compromise company accounts, confidential information, and business operations.
Thank you for your attention and cooperation in keeping our business environments secure.